30.08.2026
26 min
309


Researchers have uncovered a large-scale hacking campaign carried out by a single individual. Using 12 AI agents, the attacker targeted hundreds of organizations across 11 countries, including banks, universities, emergency services, and military systems. Some of the attacks resulted in the theft of medical records and personal data.
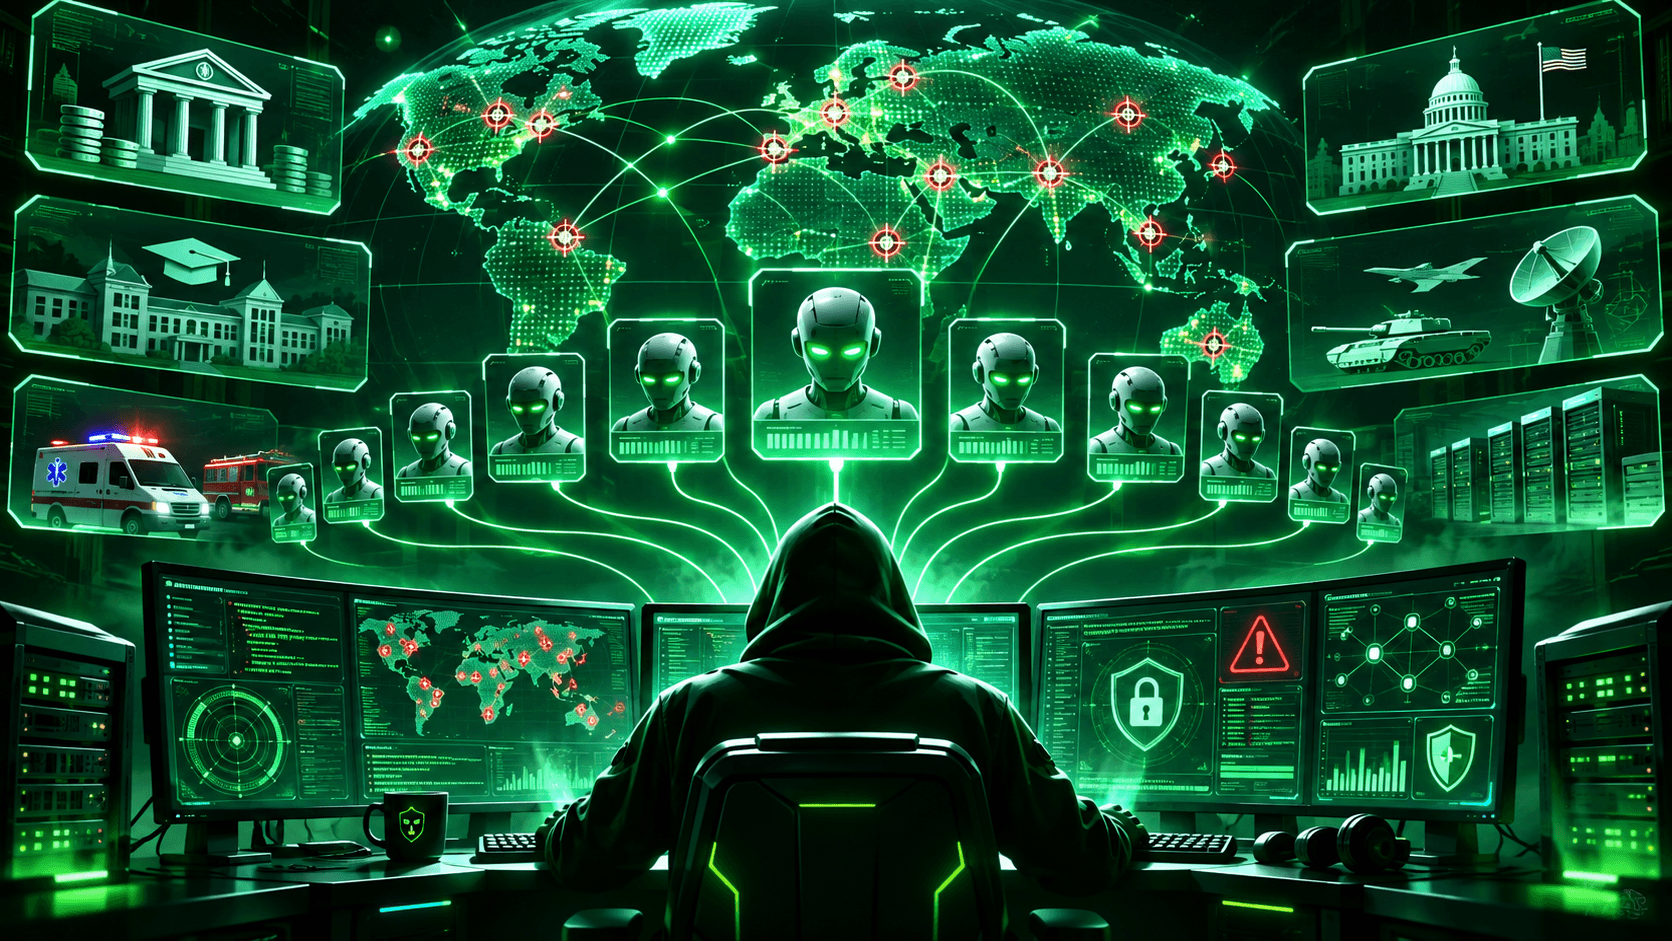
According to Acronis Threat Research Unit (TRU), the attacker built a system called BOSSAI that brought together 12 AI agents with different responsibilities. Some handled coding and infrastructure maintenance, others scanned websites for vulnerabilities, while the rest carried out attacks directly. Hundreds of organizations across 11 countries were targeted, including government emergency services, banks, credit institutions, universities, military systems, telephone directories, online stores, and gambling platforms.
Researchers believe the operator was based in Taiwan, although any potential connections to hacking groups or government organizations remain unknown. Investigators have also been unable to establish a clear motive for the campaign, but suspect the attacker aimed to compromise as many organizations as possible for financial gain. What made BOSSAI unusual was not just the number of agents involved, but how their responsibilities were divided. Instead of performing every task manually, the operator used different AI tools for individual stages of the attacks.
The campaign was discovered after Acronis researchers came across a server that initially appeared to be a misconfigured development environment. In reality, it was a fully functioning cyberattack platform. The server contained more than 90,000 files totaling approximately 9 GB, including activity logs, AI conversation histories, vulnerability exploitation tools, operator commands, and stolen victim data. These materials allowed researchers to reconstruct how the system operated and understand how one person managed such complex infrastructure.
The AI agents did not communicate directly with one another. Instead, the hacker coordinated their activities, transferred scanning results from one tool to another, and decided what actions to take next. The attacks relied on open-source automated penetration testing platforms, MCP servers, and rented GPUs. This setup allowed the operator to manage several operations simultaneously without assembling a large team.
According to Acronis TRU, the campaign’s scale resembled the operations of a well-funded hacking group, even though a single individual may have controlled the entire process. Researchers described the sophistication of the attacker’s system as follows:
“This individual built the kind of system many professionals strive to build in their day-to-day jobs.”
The researchers emphasized that such tools are typically used to automate workflows, but in this case, they were combined to conduct prolonged cyber operations.
Some BOSSAI attacks resulted in successful breaches. Researchers confirmed that universities and emergency service providers had been compromised, with personal and medical information stolen from their infrastructure. In Taiwan, for example, the attacker gained access to the Taipei Fire Department’s medical services platform. The exposed information included electrocardiograms, ambulance video recordings, and patients’ vital signs dating back to 2018. BOSSAI also obtained emergency call records from Taipei’s emergency dispatch service.
In Mexico, the AI agents collected approximately 206,800 records containing residential telephone numbers. In Thailand, the attacker identified 489 potential targets across 45 universities and managed to extract data from three of them. These incidents confirm that BOSSAI was used for more than vulnerability scanning. Some operations resulted in unauthorized access to systems and the theft of sensitive information.
Despite the sophisticated infrastructure, the operator encountered an unexpected obstacle. Commercial AI models used to build and maintain the system repeatedly refused to assist with direct attacks. According to the researchers, these models could perform supporting tasks, but requests to identify and exploit vulnerabilities were frequently blocked by safety mechanisms.
Chinese commercial models with open-source code demonstrated similar behavior. They not only refused to follow hacking instructions but also reminded the operator about cybersecurity laws. These restrictions forced the attacker to switch to locally hosted open-weight models with weakened or removed safety mechanisms.
However, these models proved less effective and required substantial computing resources. The AI agents regularly made mistakes, misinterpreted scanning results, and generated enormous amounts of information that the operator had to process. Sometimes, the agents’ excessive autonomy even interfered with the attacks. For example, one agent identified a potential target associated with a military base in Honduras but independently refused to continue, deciding that the target did not match its assigned task. As a result, while automation allowed the attacker to conduct significantly more operations, it also created new challenges in controlling their outcomes.
Acronis refers to this type of attack model as an AI-augmented threat (AAT). Its defining characteristic is that AI enables one person to carry out operations that would previously have required a team of specialists. In terms of scale and tactics, BOSSAI partially resembles the activities of advanced persistent threat (APT) groups, which are typically associated with prolonged and highly organized cyberattacks. However, in this case, researchers found no evidence of a larger team or state sponsorship.
Researchers also compared BOSSAI’s operational speed with cyber operations described in Anthropic’s research on the use of artificial intelligence by various hacking groups. At the same time, the BOSSAI case demonstrated the weaknesses of this approach. AI agents can make mistakes, deviate from assigned tasks, and create problems even for their own operator.
Nevertheless, researchers consider the campaign an indication of how cyber threats may evolve. Accessible AI models, open-source tools, and rented computing resources already allow a single individual to organize attacks against hundreds of targets across multiple countries.