

Researchers discovered serious vulnerabilities in the popular TP-Link Tapo C200 cameras that could allow an attacker with network access to the device to gain administrator privileges without a password. This could potentially give them access to the live video feed, stored recordings, and other camera functions.
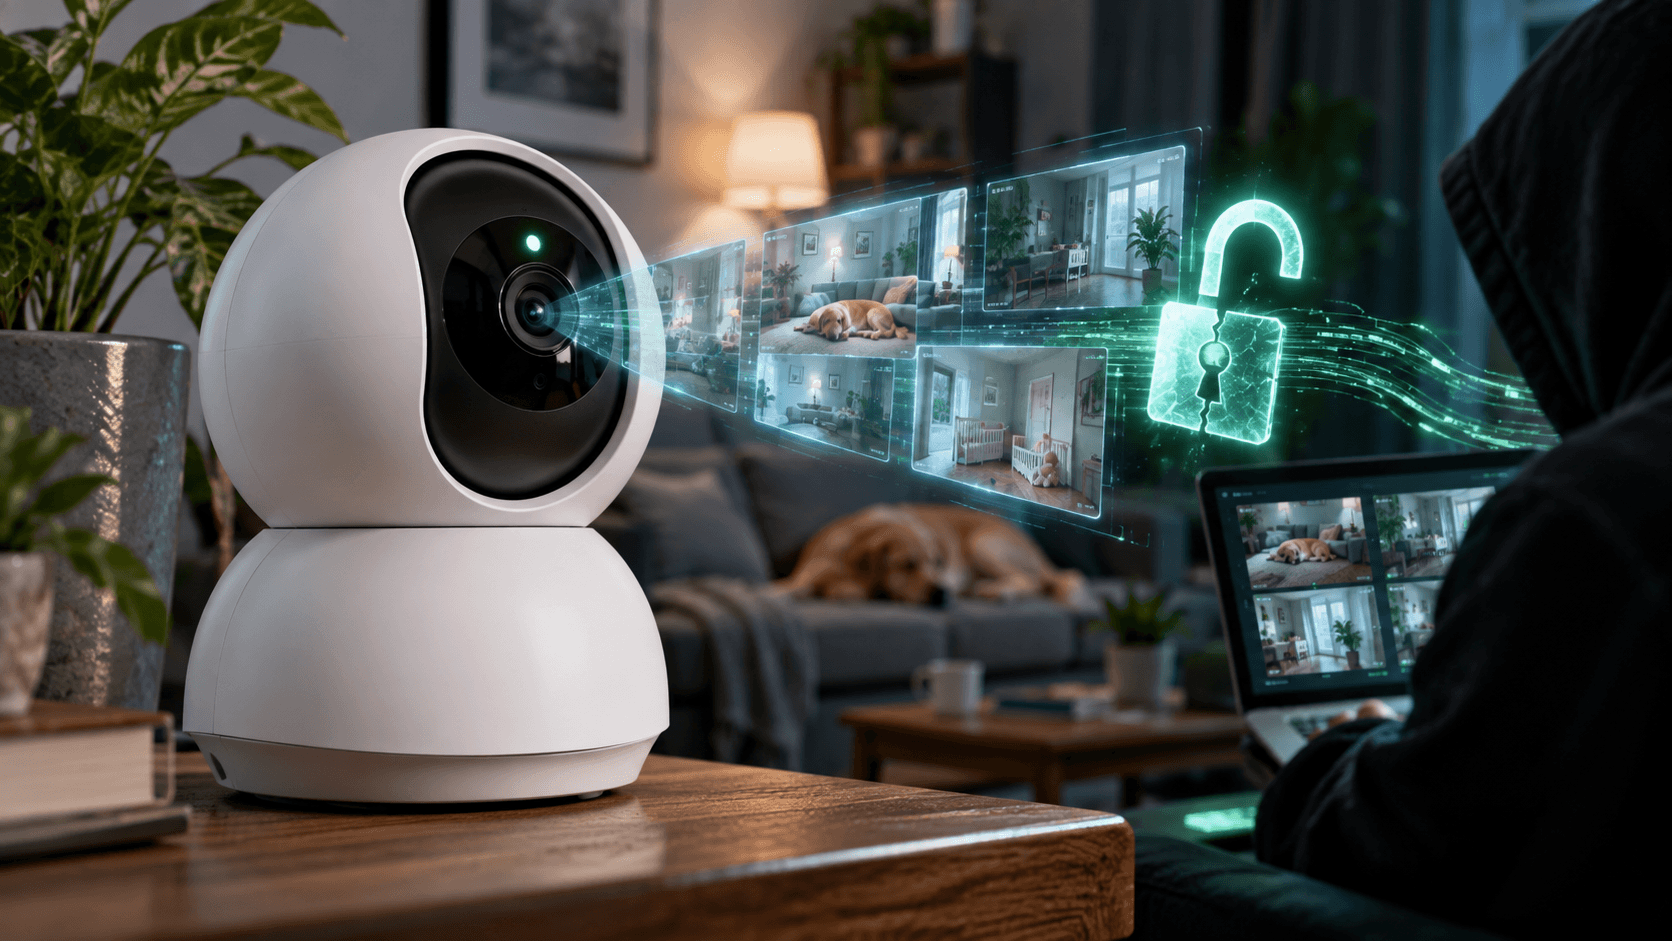
The issues were discovered by researchers at OPSWAT while analyzing the firmware of the TP-Link Tapo C200. These cameras are widely used for home surveillance, monitoring pets, and as baby monitors, as well as in some business environments.
The researchers identified three security issues. Two have already been disclosed and assigned the identifiers CVE-2026-15315 and CVE-2026-15316. Details of the third, potentially more serious vulnerability have not yet been published, as OPSWAT continues to work with TP-Link to verify and fix the issue.
One of the discovered issues, CVE-2026-15315, allowed an attacker with network access to the camera to bypass the login process and gain administrator privileges without knowing the owner’s password. The Tapo C200 uses a challenge-response authentication mechanism designed to verify whether a user actually knows the camera’s password.
However, the researchers found that certain data previously sent by the camera during authentication could be reused in a subsequent request. Due to the flaw, the system accepted this data as proof of authentication. According to the researchers, once network access was obtained, the attack required only a few malicious requests and could be completed within minutes.
After gaining administrative access, an attacker could use features normally available only to the camera’s owner. This included changing device settings, viewing the live video feed, and accessing stored recordings.
Such an attack becomes particularly dangerous when the Tapo C200 is used as a baby monitor. In that case, an attacker could potentially gain access to night vision, crying detection, and two-way audio.
As OPSWAT researchers warn:
“If the C200 camera is used as a baby monitor, an attacker could access privacy-sensitive functionality such as live video, night vision, crying detection and two-way audio.”
During the research, OPSWAT specialists discovered another issue that could potentially allow an attacker to completely take over the camera and use it as an entry point for attacks against other devices on the same network.
Technical details of this vulnerability have not yet been disclosed. OPSWAT continues to coordinate with TP-Link so the manufacturer can verify the issue and prepare the necessary fix. The researchers said additional technical details will be published once the relevant patches are available and the coordinated disclosure process is complete.
The second disclosed issue was assigned the identifier CVE-2026-15316. It is related to the handling of configuration data during the camera’s initial setup.
An attacker with network access could deliberately send a large amount of data to the device, causing the camera management service to crash. As a result, the device could become unavailable, temporarily preventing the legitimate owner from controlling it until the service recovered.
All three issues were discovered under laboratory conditions by researcher Khoi Tran, under the supervision of Thai Do, while analyzing the camera’s firmware as part of OPSWAT’s graduate program.
TP-Link released updated firmware and published security recommendations on August 18. The two disclosed vulnerabilities affect Tapo C200 cameras running firmware versions released before this update.
Owners of affected cameras are advised to install the latest firmware as soon as possible, avoid exposing their cameras directly to the internet, and properly secure their Wi-Fi networks. Businesses are also advised to isolate networks containing cameras and restrict access to authorized devices and users only.