13.08.2026
4 min
168


The popular Twitch Enhanced Viewer | JeetBot extension for Chrome and Firefox transmitted users’ active OAuth tokens through proxy servers controlled by the Russian-language bot service JeetBot. Around 31,000 Twitch users were potentially affected.
Researchers at Socket uncovered a hidden mechanism while analyzing an extension marketed as a tool for improving the Twitch viewing experience. It blocks ads, allows users to force higher video quality, bypass regional stream restrictions, and automatically collect Channel Points. These features do work, but at the same time, the extension gained access to users’ active OAuth tokens and transmitted them through infrastructure controlled by the operator.
An OAuth token is not a password, but it effectively works as a ready-made key to an already authenticated session. If a third party obtains such a token, they may not need to know the account owner’s password or go through two-factor authentication again. Depending on the permissions granted to that particular session, it could provide access to chat, private Whispers messages, Channel Points, and other Twitch features. According to Socket, the extension had around 30,000 Chrome users and another 552 Firefox users.
The process began directly on the Twitch website. Twitch’s web client uses the Authorization header for authenticated requests, and Twitch Enhanced Viewer | JeetBot read this header and passed it to the extension’s background process. The account’s OAuth token was then extracted from it.
Researchers confirmed that this was a full Twitch token rather than a separate technical key used only for video playback. The extension used it to interact with Twitch’s official token validation mechanism, further confirming the nature of the credentials it was collecting.
When the browser requested a playlist from Twitch to play a stream, the extension redirected that request through its own proxy server and inserted the OAuth token directly into the request URL as the auth= parameter. As a result, the user’s active token was sent to third-party infrastructure together with the request.
This method created an additional risk. Because the token was included directly in the request URL, it could automatically end up stored in standard proxy server logs in plain text.
Socket noted:
“Sending full account credentials exposes far more information than is required to retrieve the video.”
In other words, there is no need to transmit the full credentials of an active session simply to retrieve a video stream.
In Firefox, the redirect was implemented through webRequest.onBeforeRequest, while Chrome used the declarativeNetRequest mechanism. Despite the technical differences, the result was the same: the user’s OAuth token was transmitted to a server controlled by the extension’s operator.
The main server used by the extension was enhanced[.]jeetbot[.]cc. JeetBot presents itself as a commercial Russian-language bot service for Twitch, Kick, and VK-Live. The extension itself retrieved a list of available proxy servers from JeetBot’s server-side configuration, meaning the operator could change which server handled user traffic and, consequently, where the token was sent.
Socket linked the extension’s infrastructure to several domains and IP addresses. JeetBot’s primary domains were hosted on netcup servers in Germany, while part of the additional infrastructure used CLODO Cloud. The JeetBot website lists Popov Aleksandr Alekseevich as the operator. In browser extension stores, the extension developer uses the name HISHIMIRO. Researchers also found Russian-language comments in the source code of older versions.
Analysis of earlier versions showed that the token transmission mechanism existed before, but worked differently. In version 4.8, released on January 8, 2026, the extension sent the captured OAuth token in a separate POST request to a dedicated set-token endpoint.
The code included JeetBot’s main server and two backup addresses hosted on Deno infrastructure. Researchers also highlighted comments in the source code where, if token transmission failed, the developer instructed the program in Russian to simply ignore the error and not show the user any notification.
The code stored the last token that had been sent and enforced a five-second delay to avoid repeatedly transmitting identical data. According to Socket, this type of deduplication and rate-limiting logic makes the most sense if the server on the receiving end is storing the captured tokens.
In newer versions, the dedicated set-token endpoint disappeared, but the transmission of account credentials did not stop. Instead of sending a separate request, the OAuth token began being added directly to the request URL using the auth= parameter.
The version history on Mozilla Firefox Add-ons shows a sharp jump from version 7.2.6 in April 2026 to the 85.x branch in May. Socket found the auth= token transmission mechanism starting with version 85.2.2 and continuing at least through version 85.6.1, which was the version analyzed by the researchers.
Researchers found another unusual detail in the extension’s code. The OAuth token was sent through the proxy while users watched almost any Twitch channel, but the developers had hard-coded exceptions for ten specific channels.
The list included pch3lk1n, fasoollka, flamie, dosia, fander, almazer, forzorezor, akyuliych, lagoda1337, and lagoda. These are Russian-language Twitch channels, including several well-known figures from the Counter-Strike scene.
When a user watched one of these channels, the extension removed the OAuth token from the request before sending it through the proxy. When users watched other channels, the token continued to be transmitted. It remains unclear why these ten channels were specifically exempted.
Users were not explicitly told that their OAuth tokens would be transmitted through third-party servers. On the extension’s Chrome Web Store page, the developer states that the extension does not collect or use user data.
The privacy policy linked to the extension also claimed that it did not collect, store, or process any user data. It did not disclose the interception of Twitch OAuth tokens or their transmission to third-party infrastructure. Socket says the extension’s actual behavior directly contradicts those claims.
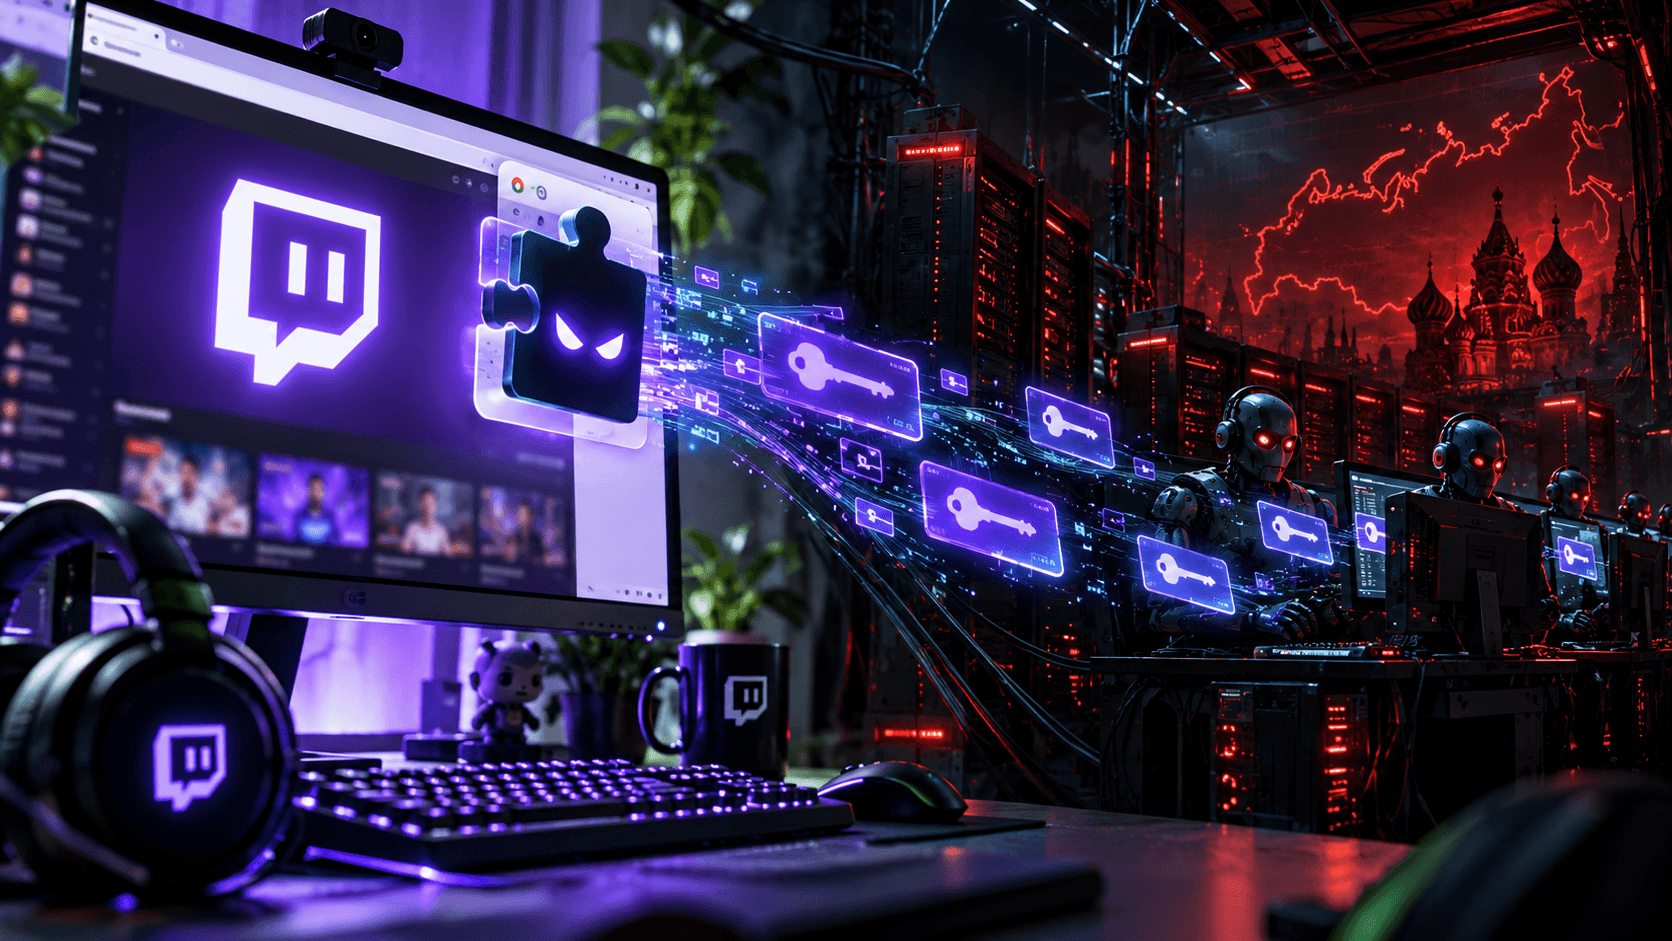
Around 31,000 Chrome and Firefox users may have had active OAuth tokens from their Twitch accounts transmitted through infrastructure controlled by the extension’s operator. Such a token effectively proves that its holder is already authenticated, which means a third party with a valid token may not need the account password or a new two-factor authentication challenge.
Among the actions potentially available through such a token, Socket lists reading and sending Whispers, posting messages in chat, using Channel Points, and interacting with other account features depending on the permissions granted to the specific session.
At the same time, the fact that tokens were transmitted does not mean that all 31,000 accounts were actually taken over. The research confirms that account credentials were routed through infrastructure controlled by the operator, meaning affected users were potentially compromised.
Socket recommends removing Twitch Enhanced Viewer | JeetBot from Chrome or Firefox. However, simply uninstalling the extension may not be enough if the OAuth token has already been sent to a third-party server. After removing it, users should open their Twitch settings, terminate all active sessions, and then sign in again. This invalidates previous session tokens, including any that may have been transmitted through the proxy.
For corporate and security-sensitive environments, specialists also recommend checking devices for the presence of the extension and blocking the identified infrastructure at the network level.
The Twitch Enhanced Viewer | JeetBot case once again shows how much access an ordinary browser extension can obtain. Extensions deserve particular scrutiny when they have access to authenticated services while also routing traffic through third-party servers.