

Researchers have demonstrated a new hardware attack called DDRop that can undermine confidential computing protections on modern Intel and AMD servers. The attack requires only a device costing less than $200, installed between the processor and a DDR5 memory module.
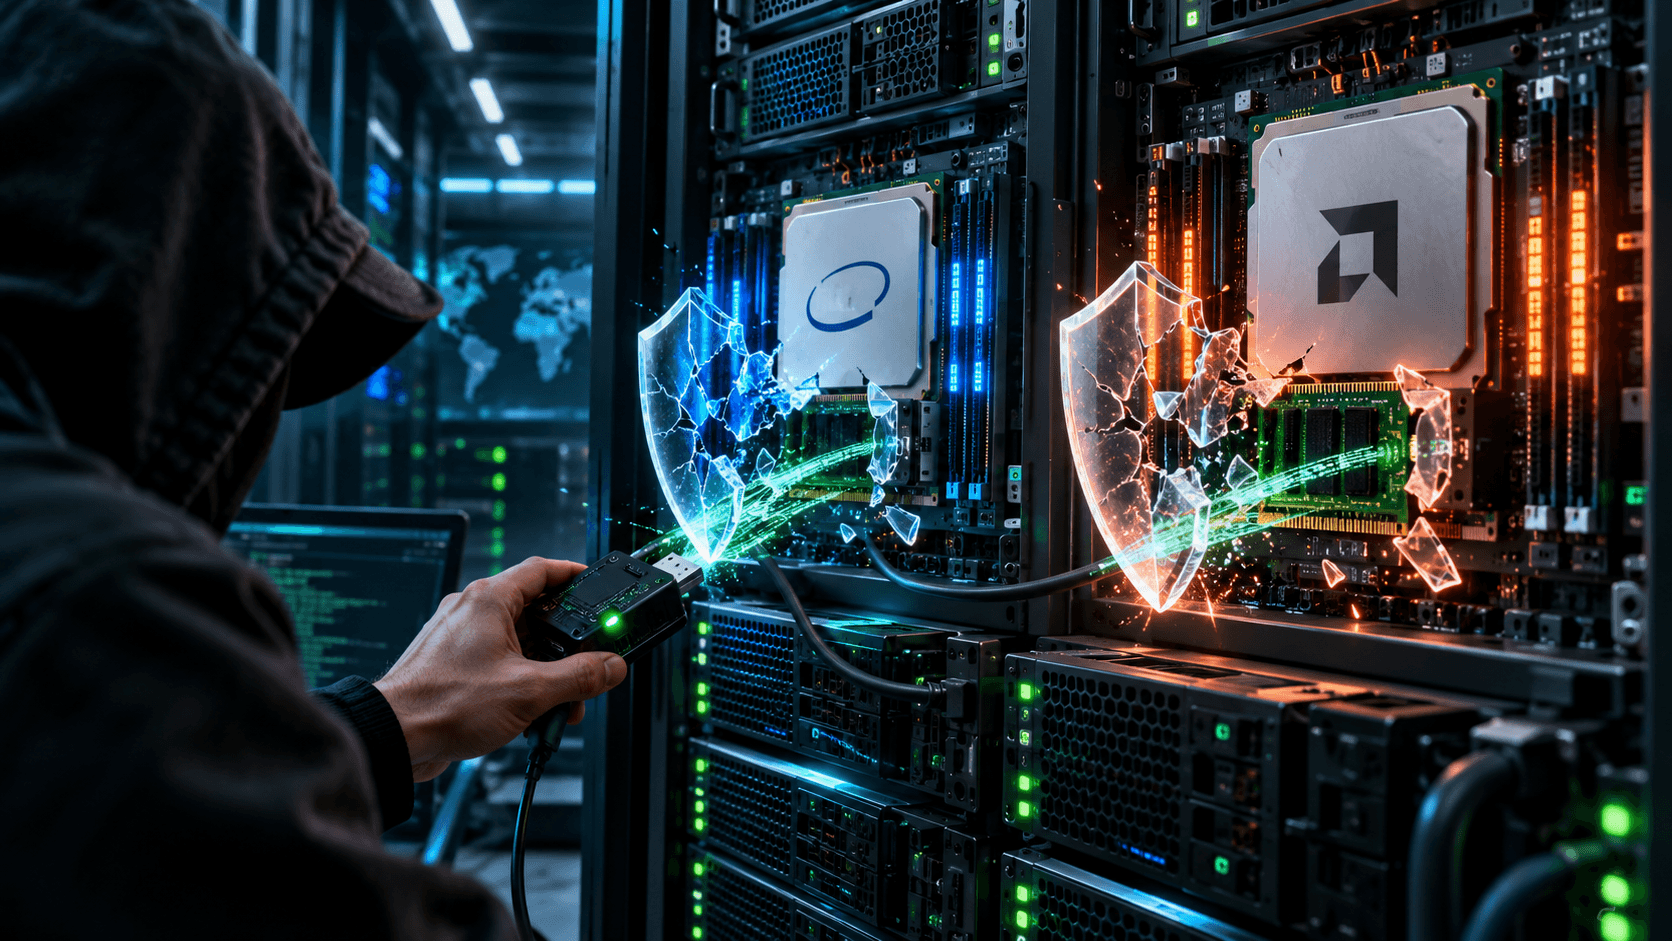
Researchers from KU Leuven, ETH Zurich, Durham University, and Google developed the DDRop attack against confidential computing technologies. These systems are designed to protect sensitive data even when an attacker already controls the server’s operating system or hypervisor. The researchers tested the attack against Trusted Execution Environments, or TEEs, including Intel TDX, Intel Scalable SGX, and AMD SEV-SNP. A detailed description of DDRop, technical materials, and experimental results were published by the authors on the official research website.
The key component is a low-cost hardware adapter, known as an interposer, installed directly between the processor and the DDR5 memory module. The device costs less than $200. DDRop can selectively block write operations to RAM, causing the processor to continue reading old encrypted data while treating it as current. This exposes a weakness in modern confidential computing systems: they can verify that data is authentic and has not been tampered with, but they cannot always determine whether it is the most recent version.
The most serious demonstration targeted Intel TDX. By manipulating protected page-table data, the researchers were able to force a confidential virtual machine into debug mode and then read its private memory in plaintext.
The issue stems from a trade-off between security and performance. TEEs use hardware isolation, remote attestation, and transparent memory encryption to protect workloads in cloud environments. However, full cryptographic verification of the freshness of every memory write would add extra overhead to systems that need to process huge volumes of data with minimal latency.
The study’s authors explain that, in order to maintain the required performance and support large amounts of memory, modern TEEs do not use a cryptographic mechanism that guarantees the freshness of every memory entry. As a result, the system may fail to detect when old but correctly encrypted data is replayed. This is what makes replay attacks possible when an attacker gains physical access to a server’s memory.
Fixing the problem with a regular software update is difficult. DDRop exploits the physical interaction between memory and the processor, meaning a software patch cannot eliminate the underlying hardware cause of the attack. Intel and AMD were informed of the research through coordinated disclosure and confirmed the findings. At the same time, both companies noted that DDRop requires physical access to the server and that such attacks are outside their published threat models.
Confidential computing is used to protect highly sensitive data in cloud infrastructure. The idea is to isolate data not only while it is stored or transmitted, but also while it is being processed by the CPU. This means that even a host-system administrator or an attacker who gains control of the hypervisor should not be able to read the contents of a protected virtual machine. DDRop shows that physical interference with memory operations can bypass some of these guarantees.