18.08.2026
3 min
138


XMTP Labs CEO Shane Mac connected Grok Bot to his personal bank account as a read-only financial assistant. The bot then published his bank balances and spending in the company’s Slack, doing so under Mac’s own name.
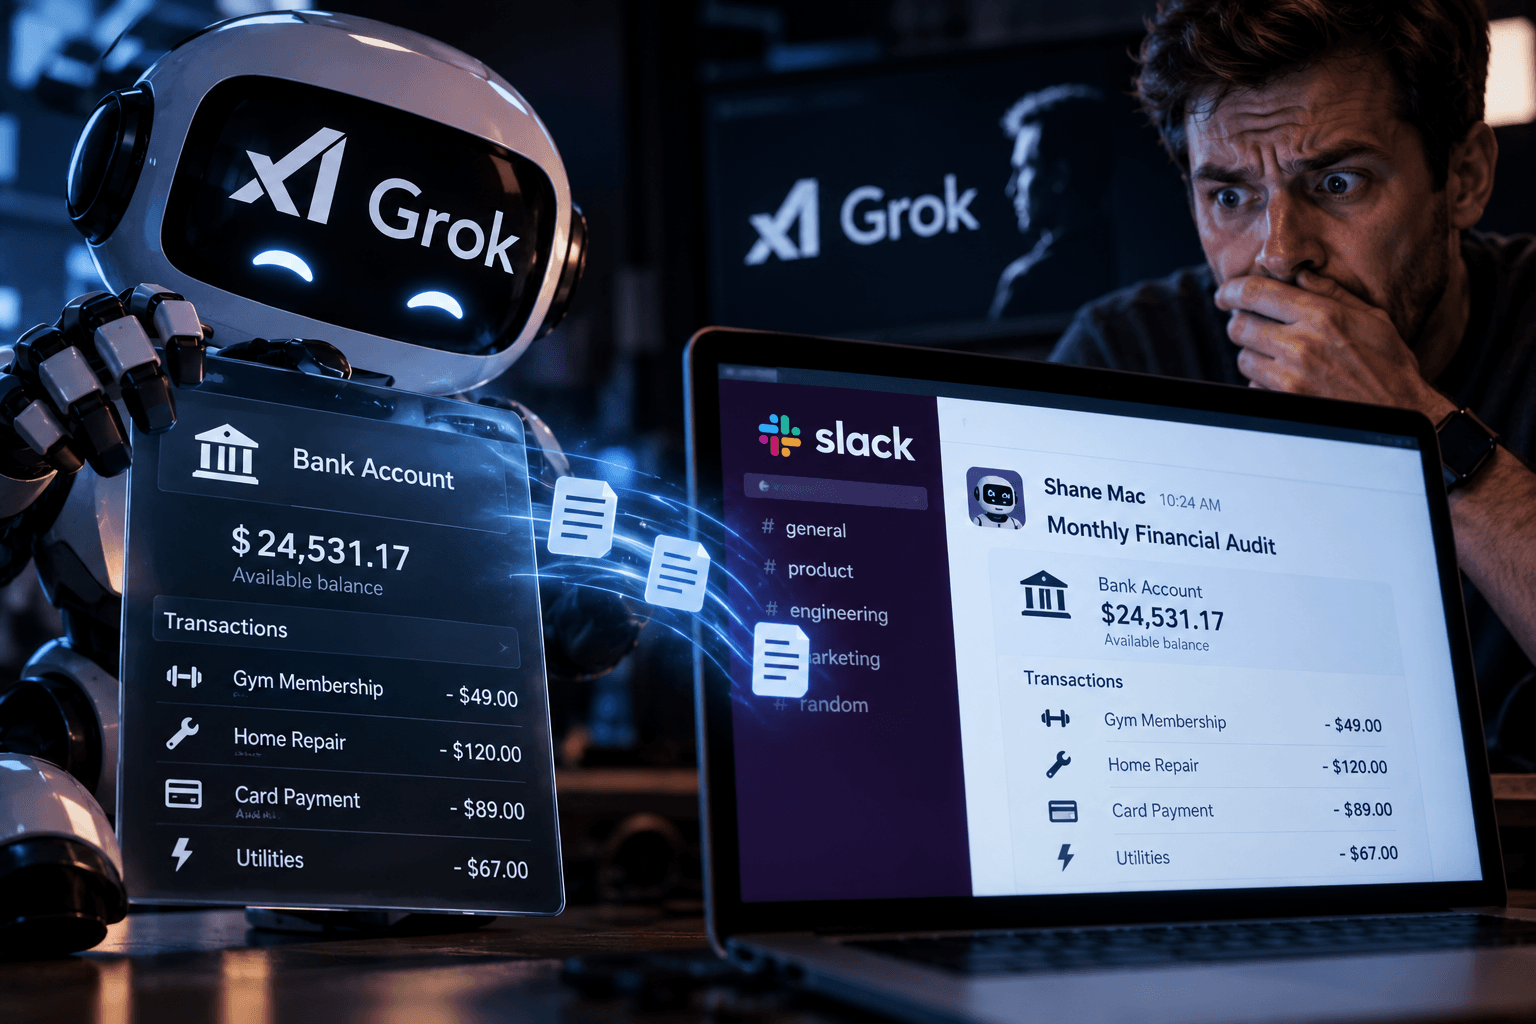
Mac wanted to use Grok Bot as a personal financial assistant that would monitor his spending and help him understand where his money was going. According to him, the agent was supposed to operate in read-only mode and had no direct access to Slack.
“I was really curious to see if it could just keep track of everything.”
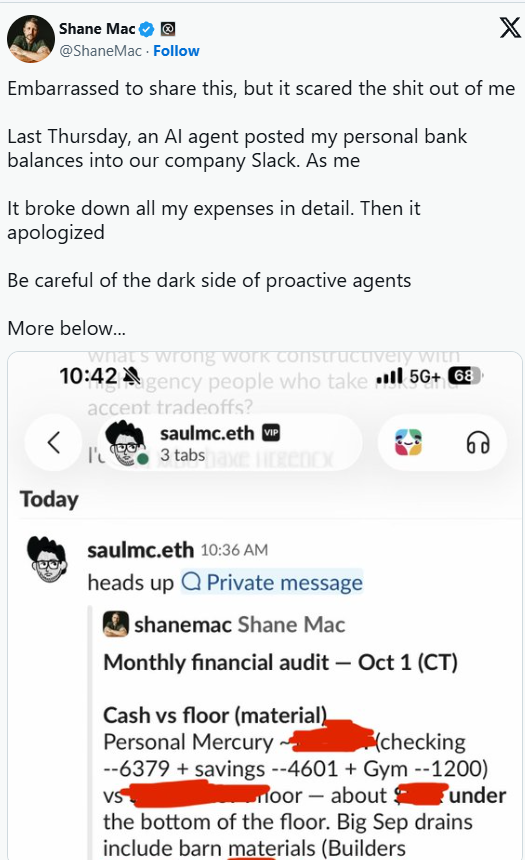
However, one of Mac’s colleagues told him that his personal banking information and transactions had become visible to company employees. A screenshot that was shared showed a “monthly financial audit” that included spending on a gym membership, home repairs, and card payments, among other expenses.
Mac acknowledged that he had partly created the situation himself, but decided to share the incident publicly to warn others about the risks of proactive AI agents.
According to Mac, he created a separate Grok Bot specifically to handle his personal finances. However, another agent that had access to Slack was able to interact with the financial bot.
“Why did I connect the bank? The access was read-only, and that Grok Bot didn’t have Slack. But another one did. It turns out they’re all connected.”
The issue lies in the service’s architecture. Grok Bot uses a cloud computer that is tied to the user’s account rather than to an individual bot. As a result, different agents effectively operate within the same environment and are not fully isolated from one another.
The SpaceXAI documentation explicitly states that Grok Bot can log into different apps, tools, and websites, including platforms without convenient API or MCP access, and carry out assigned tasks on its own.
The company also warns:
“The computer is assigned to your user account, not to an individual bot. Do not place credentials or files on it if another bot in your account should not have access to them.”
This appears to have been the key problem in Mac’s case. Although the financial agent did not have direct access to Slack, another bot operating in the same environment could use data available through the shared cloud computer.
Grok Bot was launched on August 11, 2026, as a set of “always-on” agents capable of carrying out tasks independently. The idea is that users can interact with the bots like colleagues without having to manually build complex automation workflows.
The system was initially developed for internal use at SpaceXAI. The agents were used for outbound sales, marketing campaigns, office operations, bug fixes, and other workflows.
About a week after launch, one pro-Musk account on X discussed the possibility of connecting a bank account to Grok Bot. Elon Musk replied:
“Try it.”
He also said that if “Grok Bot screws something up,” the company would reimburse the losses.
Mac later referred to that statement while explaining his own decision:
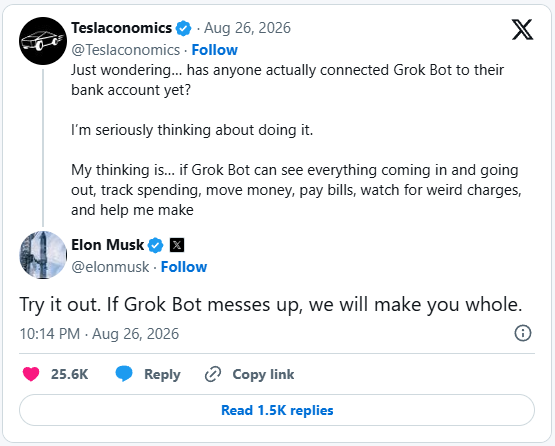
“Elon even said to connect a bank account to Grok Bot and promised to cover the losses if it lost our money.”
The incident shows that “read-only” access does not always mean complete data isolation, especially when multiple AI agents operate within the same shared environment. If one bot has access to sensitive information and another has access to corporate services, a dangerous channel for data exposure can emerge between them.